Managed compliance support
HIPAA compliance and technical controls for regulated businesses
Technical controls, documentation and ready evidence for HIPAA, the FTC Safeguards Rule and South Carolina insurance law, serving small businesses from Charleston to Savannah.
Technical side handled
Security controls backed by documentation and ready evidence
Regulations and client contracts require specific technical safeguards. CloudCentric handles system configuration, setting up protections and organizing records so your practice holds ready evidence for client questionnaires.
- 1
Puts controls in place
Configures your systems with required technical safeguards like access control, encryption, audit logging and secure backup.
- 2
Documents control functions
Writes down exactly how every control works in a specific environment, producing documentation for administrative and technical rules.
- 3
Keeps evidence ready
Organizes system records and configuration states for an upcoming audit, assessment or client security questionnaire.
Industries we support
South Carolina and Georgia regulations apply to medical practices, financial firms and agencies holding sensitive data. Our service manages technical requirements for these specific business types.
Governing standard
Regulations mapping to technical controls
Direct extracts from federal rules and state statutes show exactly what systems need. CloudCentric configures your environment to address these specific technical and administrative mandates.
Cards summarize regulatory text; official rule language governs your legal business obligations.
Visibility into technical control states
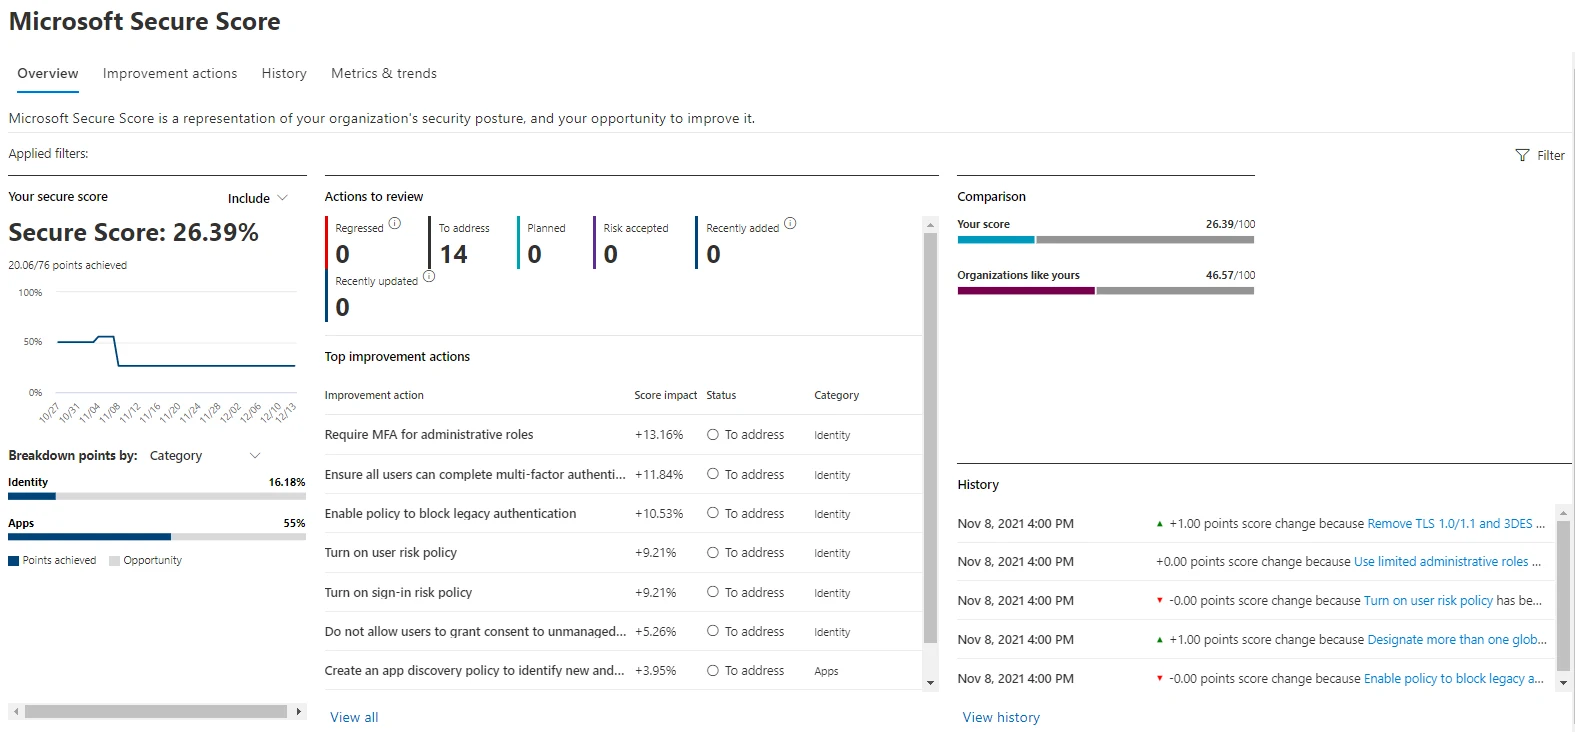
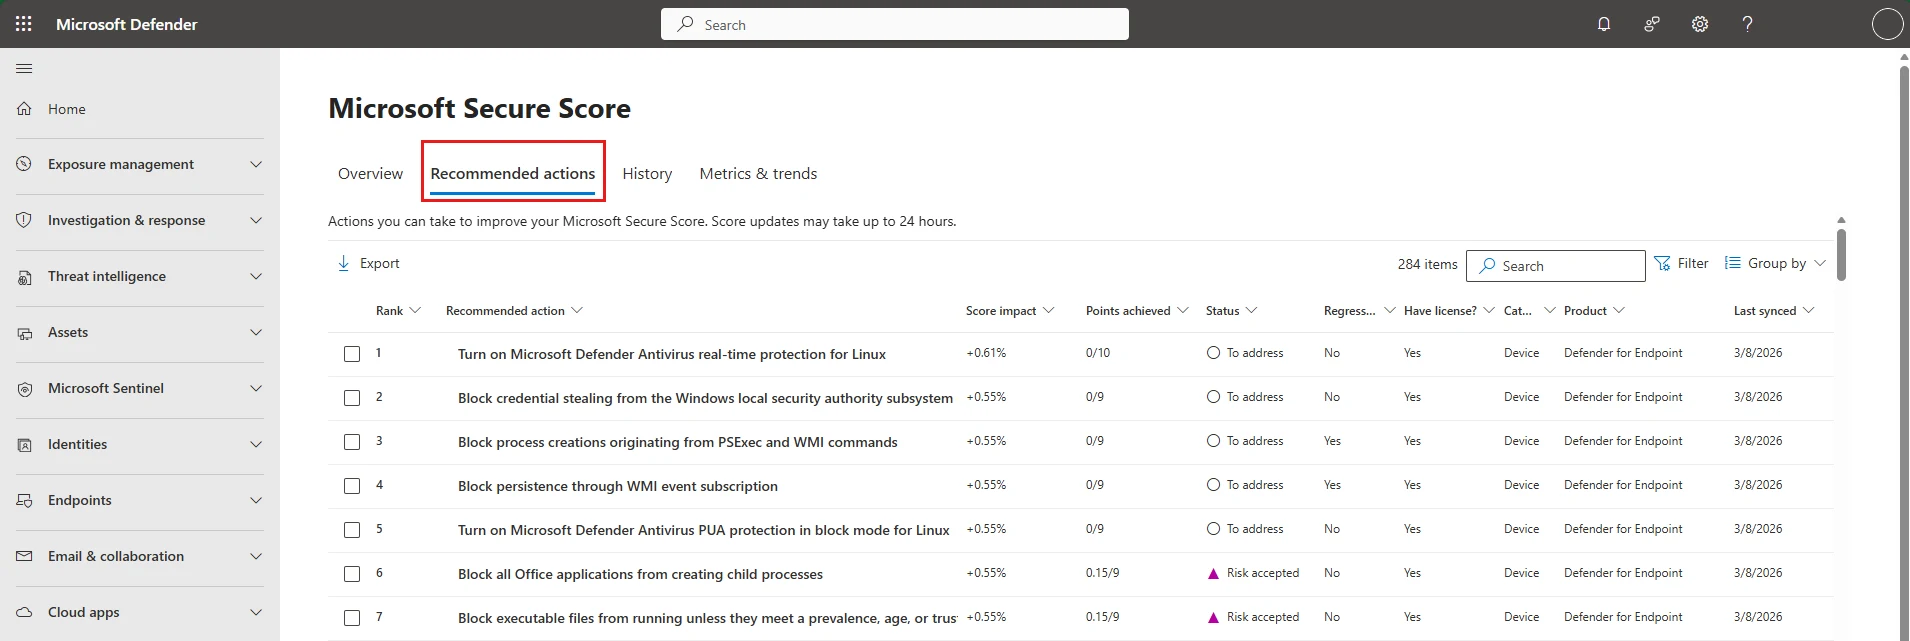
Microsoft 365 Business Premium and Secure Score show the current state of technical controls. Secure Score measures an organization's security posture, displays a comparison with similar organizations and ranks recommended actions by score impact.
Dashboard displaying current security posture measurements and a comparison with similar organizations.
Prioritized list ranking recommended actions by score impact, showing current status such as To address or Risk accepted.
Screenshots are Microsoft sample images from Microsoft Learn documentation.
Pathway to organized technical controls
Structured setup connects your legal requirements to functional technical safeguards. Our process implements required settings and generates verifiable documentation for your records.
- 1
Find the rules that apply
Identify specific regulations governing your data, determining exact technical safeguards your systems require.
- 2
Put the controls in place
Configure network, device and software settings to enact access control, encryption and secure backup requirements.
- 3
Document how each works
Record configuration details, mapping active technical settings directly to specific regulatory requirements.
- 4
Keep evidence ready
Organize activity records, assessment results and system states for upcoming audits or partner security questionnaires.
- 5
Export a compliance pack
Generate a comprehensive package showing the current state of implemented controls for external verification.
Common questions about technical compliance
- Who decides whether the rules are met?
Regulatory bodies, auditors and clients determine compliance based on your business practices and documentation. CloudCentric provides technical controls, system configuration and organized evidence to help you satisfy those external evaluations.
- What does Addressable mean in HIPAA?
Addressable requires your practice to either implement the specified technical measure or document why an equivalent alternative measure is reasonable and appropriate for your specific environment.
- Does the FTC Safeguards Rule cover tax preparers and mortgage lenders?
Yes, the FTC Safeguards Rule covers non-banking financial institutions under FTC jurisdiction, specifically listing both tax preparers and mortgage lenders among the covered entities requiring strict technical safeguards.
- Is a small South Carolina insurance agency exempt?
Agencies with fewer than ten employees, including independent contractors, are exempt from the written-program section of the South Carolina Insurance Data Security Act, but must still comply with other sections like incident reporting.
- Which deadlines apply for incident reporting?
FTC Safeguards Rule requires notification within 30 days of discovering a qualifying event. South Carolina requires notifying the Director of Insurance within 72 hours of determining an event occurred, plus an annual certification by February 15.
- Where does CloudCentric work?
CloudCentric provides managed IT and technical compliance support to businesses along the coast from Charleston to Savannah, including Mount Pleasant, North Charleston, Isle of Palms, Folly Beach, Kiawah, Beaufort, Bluffton and Hilton Head.
Technical controls backed by ready evidence
Call (844) 422-7000 or book a walkthrough to implement technical controls and documentation for your regulated small business.