Defense contractor IT
CMMC compliance readiness for Lowcountry defense suppliers
We put technical controls in place in Microsoft 365, write your documentation and keep evidence ready for defense contractors from Charleston to Savannah.
Technical readiness
Preparing your Microsoft 365 environment for assessment
CloudCentric handles your technical requirements for defense contracts. Our team configures your tenant, records your system security plan and organizes your assessment artifacts.
- 1
Puts NIST SP 800-171 controls
We configure technical settings in Microsoft 365 to meet the required defense standards.
- 2
Documents how each control works
Our team writes down your operational procedures and details your exact configurations for your system security plan.
- 3
Keeps evidence ready for assessment
Assessment requires proof of practice. We collect and organize your logs and compliance records so your affirming official is prepared.
Requirements prime contractors pass to subcontractors
Prime contractors pass specific security requirements to their subcontractors based on Federal Contract Information and Controlled Unclassified Information.
Applicable CMMC level
Requirements for CMMC Level 2 and other tiers
Department of Defense programs select your required tier based on your handled data. Review your target tier to see your operational and assessment obligations.
Cards summarize 32 CFR part 170. Official rule text governs your exact legal requirements.
Tracking evidence in Microsoft Purview Compliance Manager
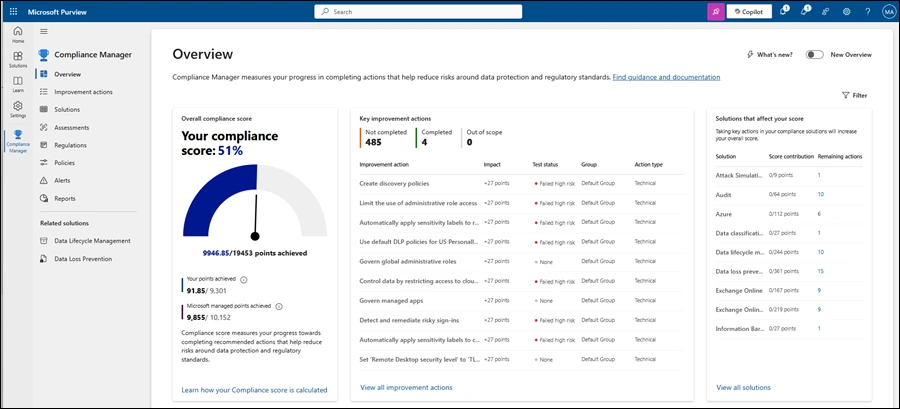
Microsoft Purview Compliance Manager provides assessment templates, a compliance score and improvement actions that hold evidence. CMMC levels are included for GCC Moderate, GCC High and DoD customers and listed among premium regulations otherwise.
Compliance Manager overview displaying the overall compliance score, key improvement actions with their impact and test status.
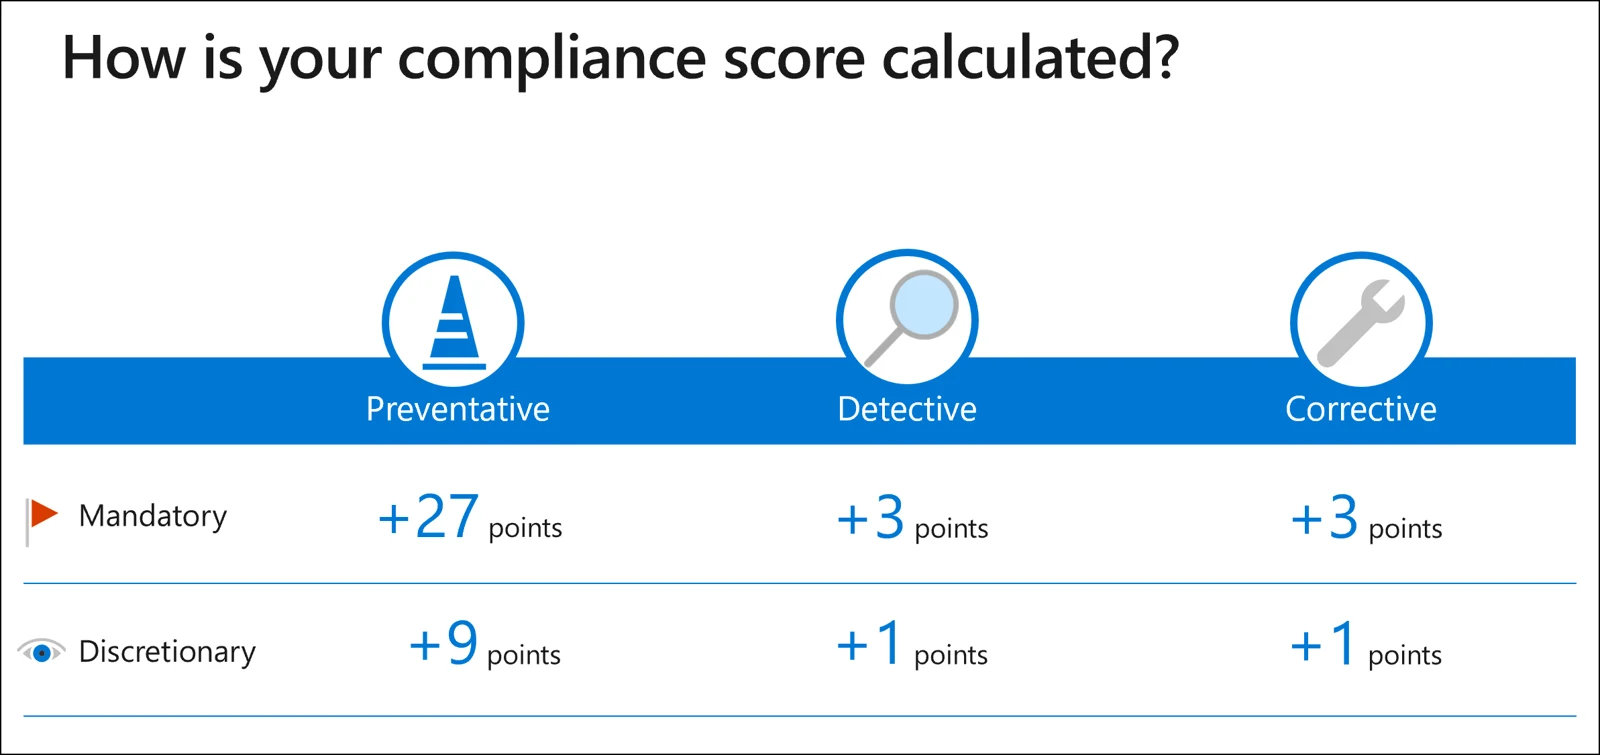
Microsoft graphic showing points categorized by preventative, detective and corrective actions, both mandatory and discretionary.
Interface screens are Microsoft's own provided from Microsoft Learn documentation.
Implementing NIST SP 800-171 controls for your systems
CloudCentric prepares your environment by configuring tenant settings and gathering documentation. Our team structures your administrative tasks ahead of evaluation.
- 1
Find the required level
Consult your contract solicitation to identify your required status based on handled federal data.
- 2
Scope the targeted systems
Identify infrastructure, external service providers and cloud resources processing, storing or transmitting federal information.
- 3
Put controls in place
CloudCentric configures technical settings within your Microsoft 365 environment to satisfy your targeted tier.
- 4
Write the plan down
Our team records your system security plan and organizes your artifacts to keep evidence ready.
- 5
Support the assessment
A C3PAO assesses at Level 2. Your senior affirming official reviews the evidence and affirms compliance.
Common questions about compliance readiness
- Who performs the Level 2 certification assessment?
A CMMC Third-Party Assessment Organization (C3PAO) performs a Level 2 certification assessment. The Cybersecurity Maturity Model Certification Accreditation Body, Inc. (Cyber AB) authorizes and ensures their accreditation.
- Will a CMMC consultant certify my company?
No outside consultant certifies a contractor. A C3PAO performs the Level 2 certification assessment, while your own senior representative serves as the affirming official who affirms continuing compliance.
- Do subcontractors need CMMC status?
Prime contractors flow requirements down to subcontractors at all tiers that process, store or transmit covered data. Handlers of Controlled Unclassified Information need at least Level 2 (Self).
- Does Microsoft 365 meet CMMC requirements, and do I need GCC High?
Compliance Manager lists CMMC templates. Cloud providers must meet FedRAMP Moderate equivalent security. Which Microsoft cloud fits your business is decided together based on your data and contracts.
- What is a Plan of Action and Milestones (POA&M)?
A POA&M addresses specific unmet requirements under a Conditional status. It must be closed out within 180 days of the Conditional status date, or the status expires.
- Where does CloudCentric offer technical services?
CloudCentric serves businesses across Charleston and the Lowcountry, covering Mount Pleasant, North Charleston, Isle of Palms, Folly Beach, Kiawah, Beaufort, Bluffton, Savannah and Hilton Head.
Readiness for defense contractors
Call our team to prepare your Microsoft 365 environment for assessment.