Being exploited now
Flaws actively used by attackers are flagged first using the CISA KEV catalog.
Managed IT services
CloudCentric checks computers, servers and websites against known flaws for businesses across Charleston and the Lowcountry, prioritizing vulnerabilities actively exploited in the wild.
Device and software inventory
CloudCentric provides a running list of your machines and software, each checked against CVEs. Exposed systems are ranked by severity so work begins in the right place.
Inventories record devices and software, alongside browser extensions and digital certificates, across your organization.
Each listed item is checked against the public list of known flaws to identify exposure.
Exposures are ranked by severity so you and our team know where remediation work begins.
Auditors, clients and insurance applications ask how businesses find out what is out of date. Vulnerability scans provide evidence for these requirements.
Requirement or question
Jump to scanner views
CloudCentric uses Microsoft Defender Vulnerability Management to check systems. Screen captures show how devices and known flaws are listed and tracked.
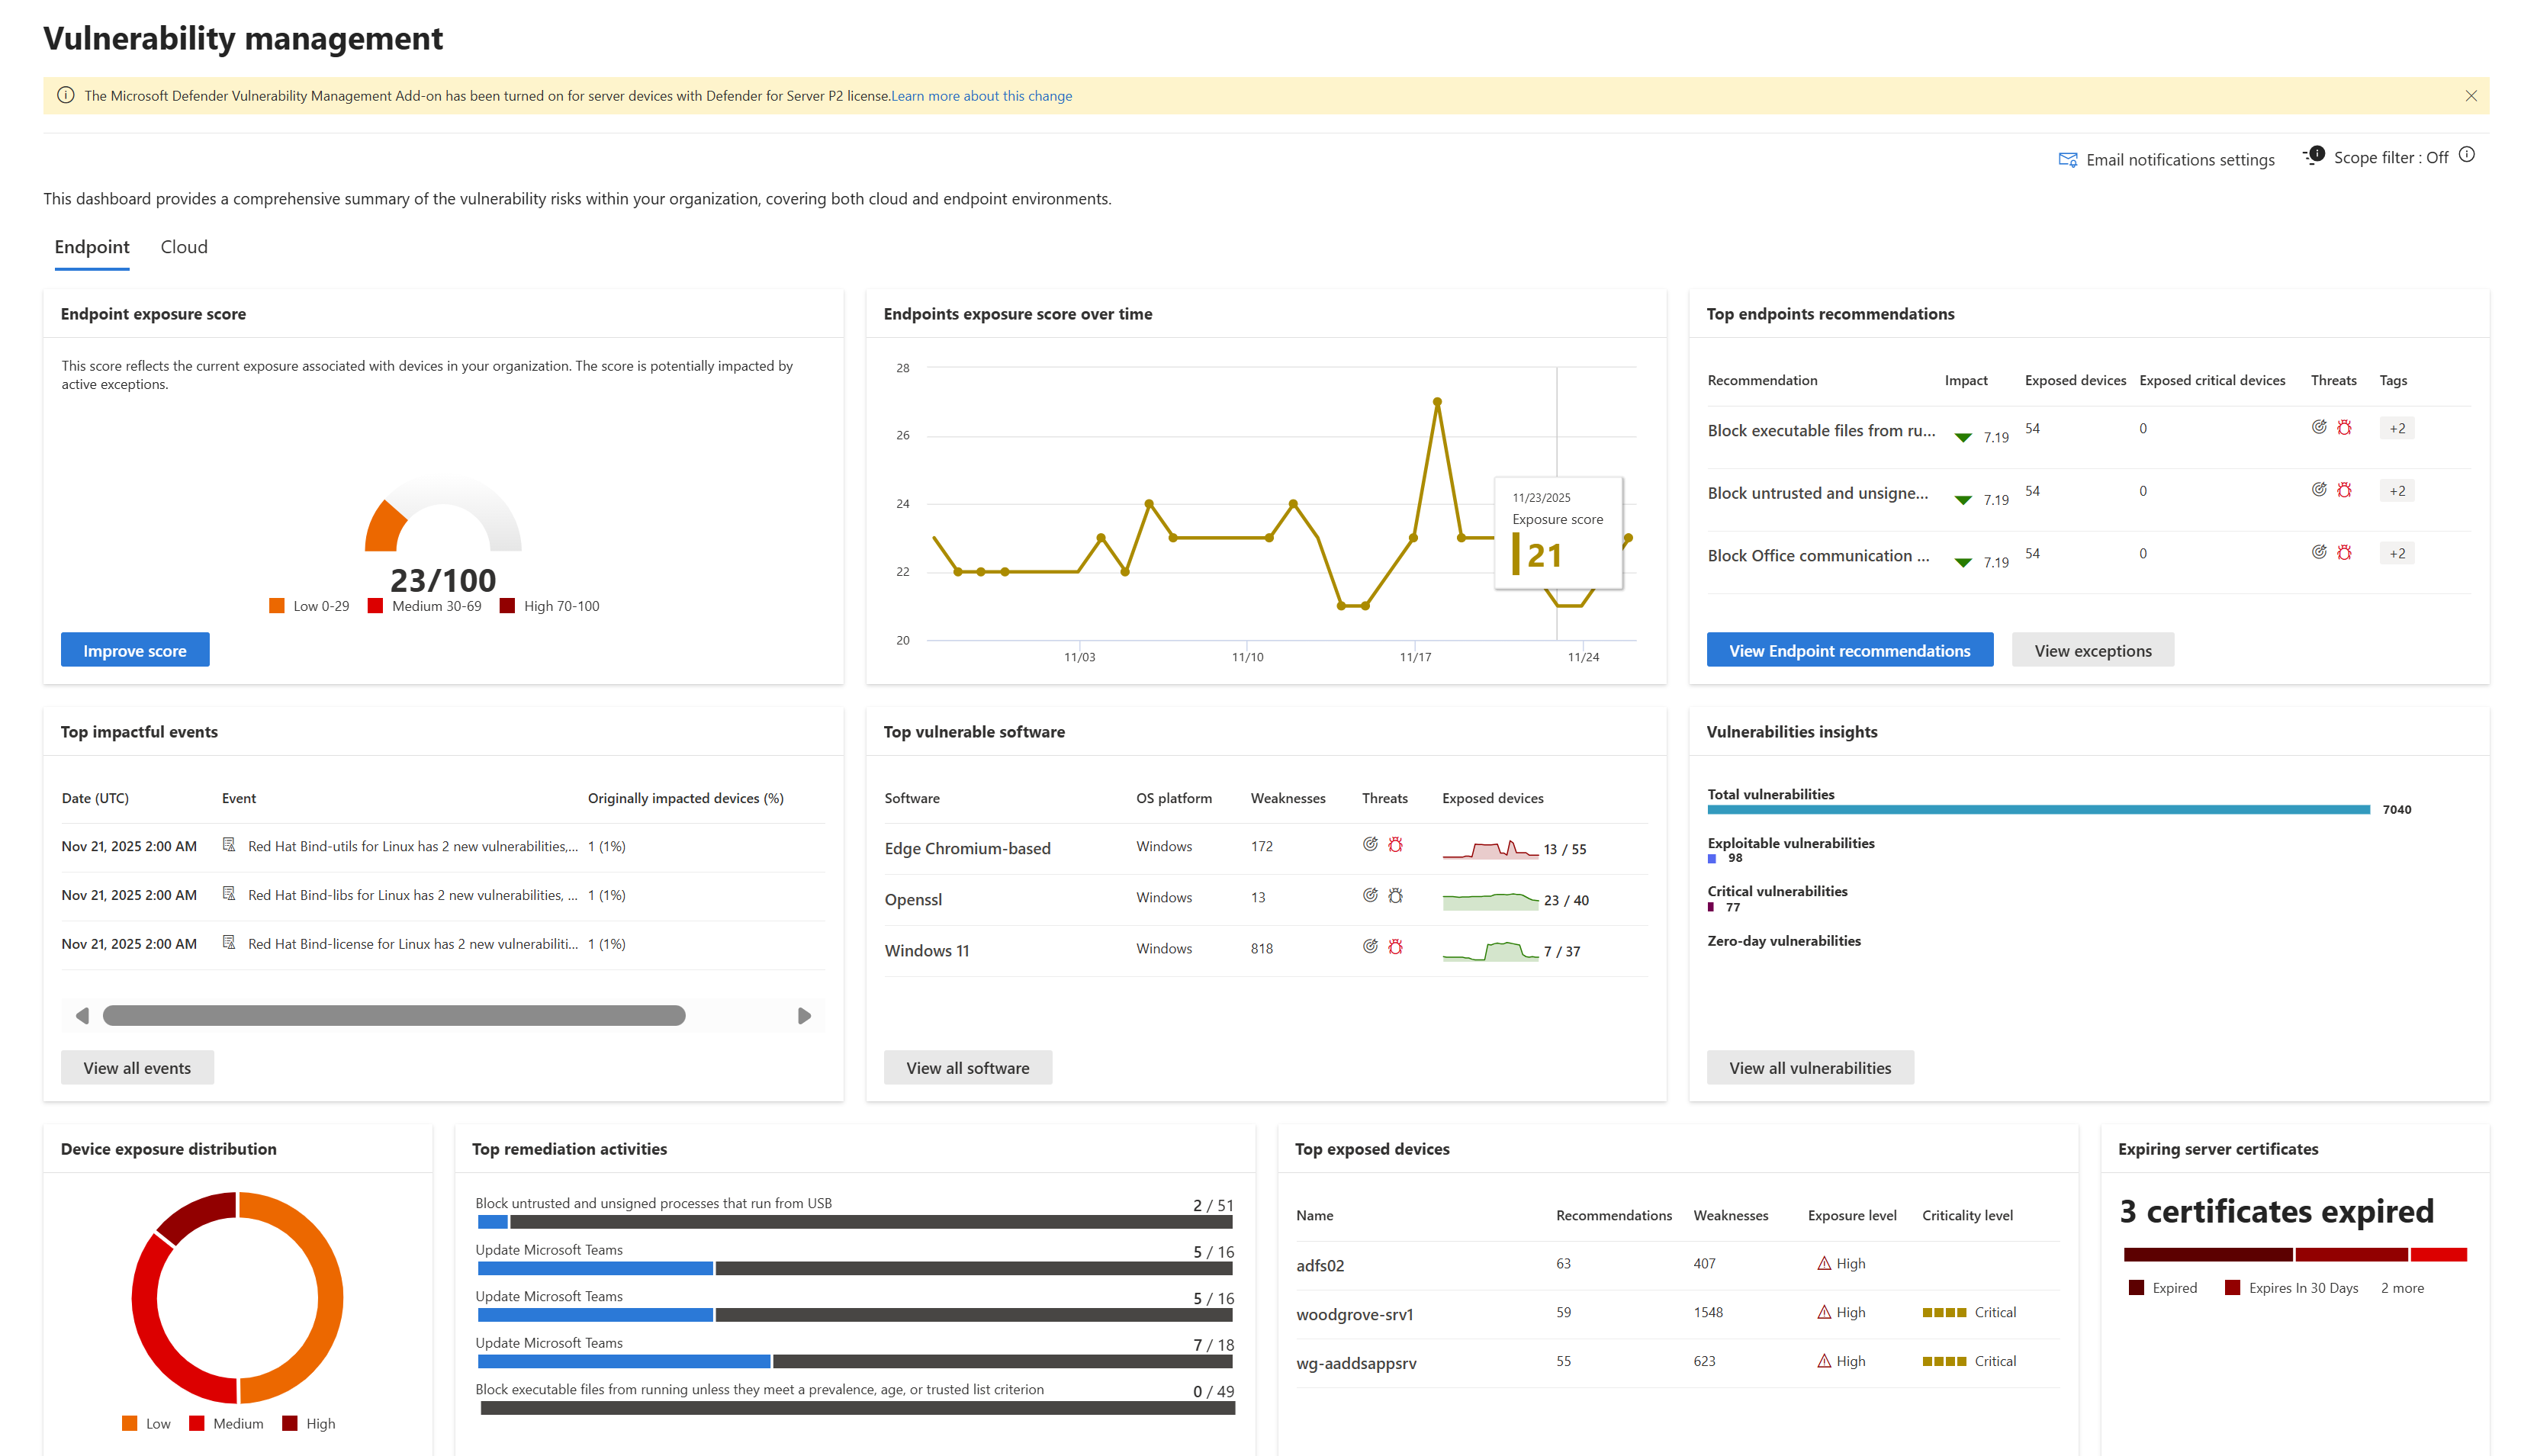
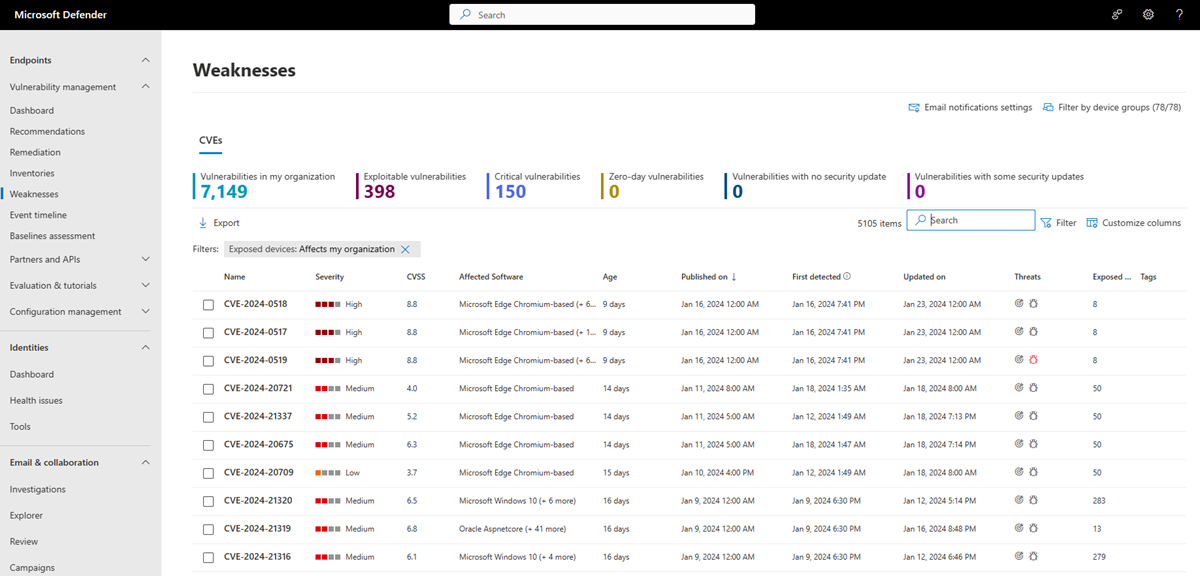
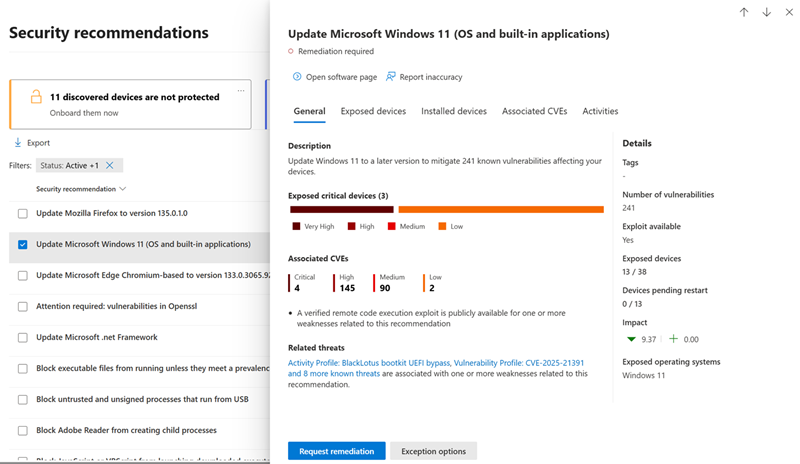
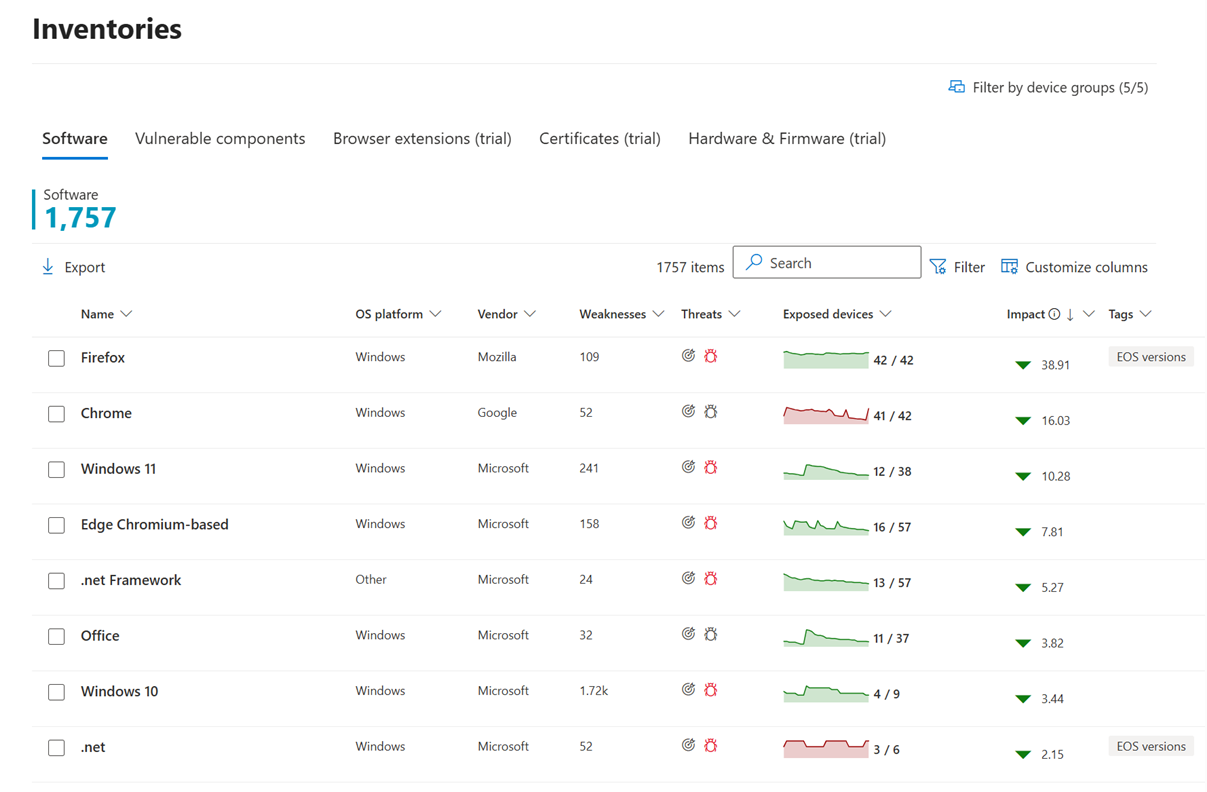
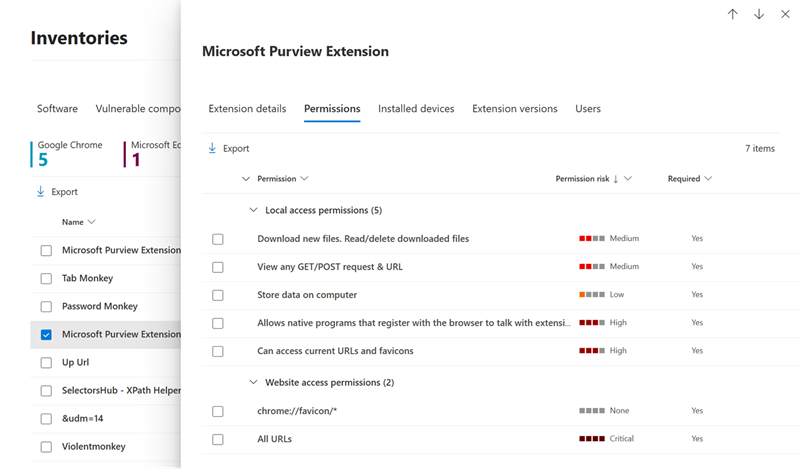
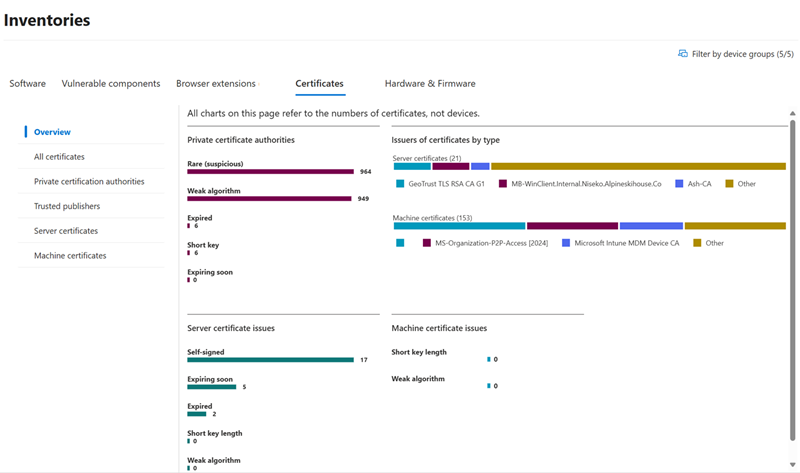
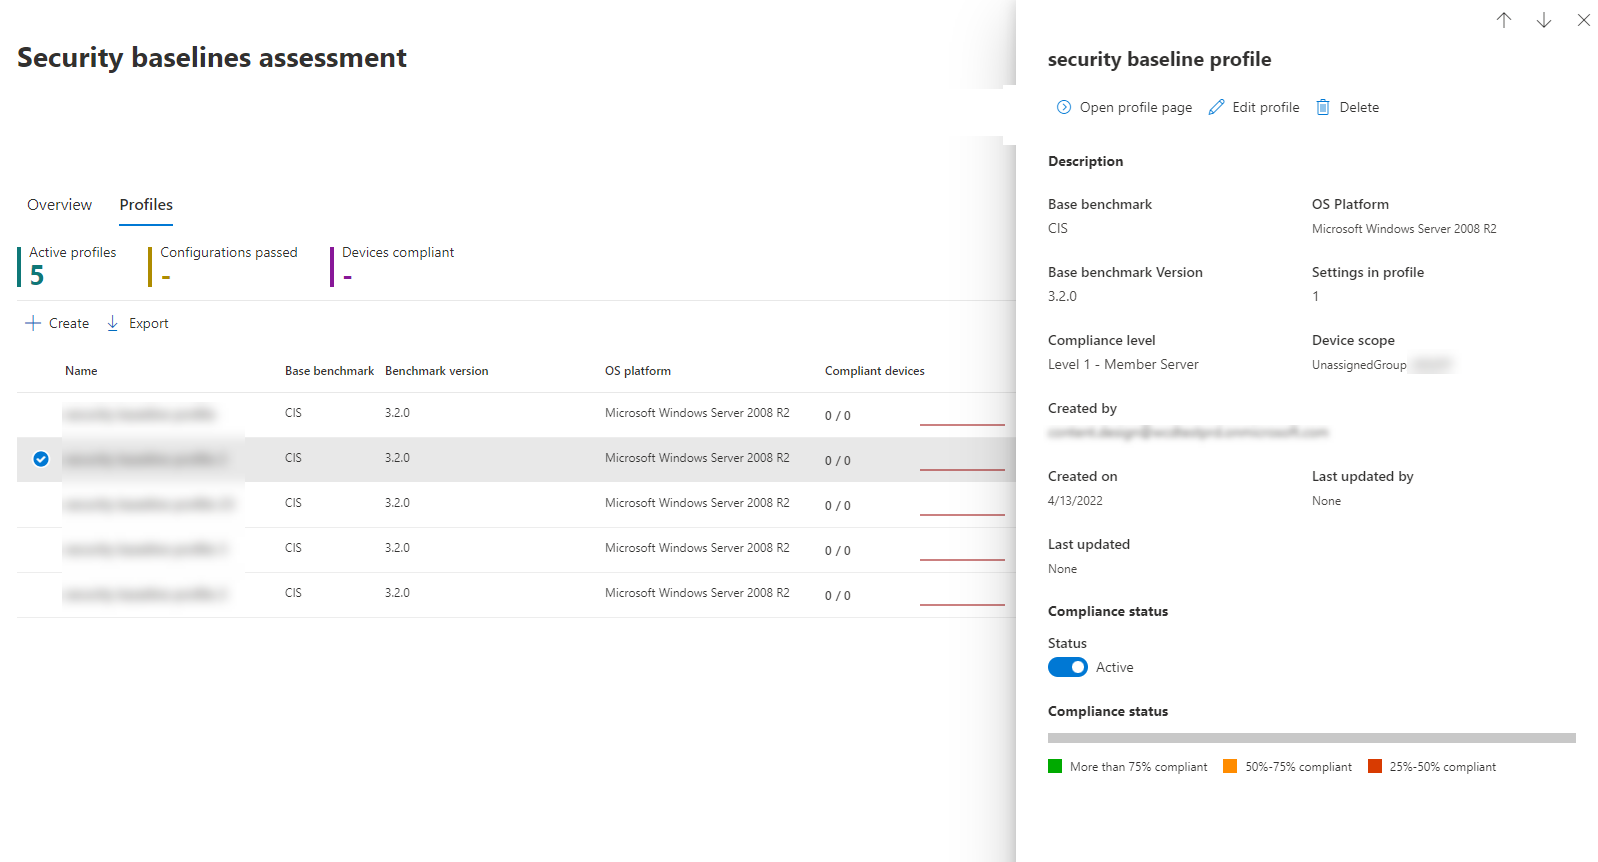
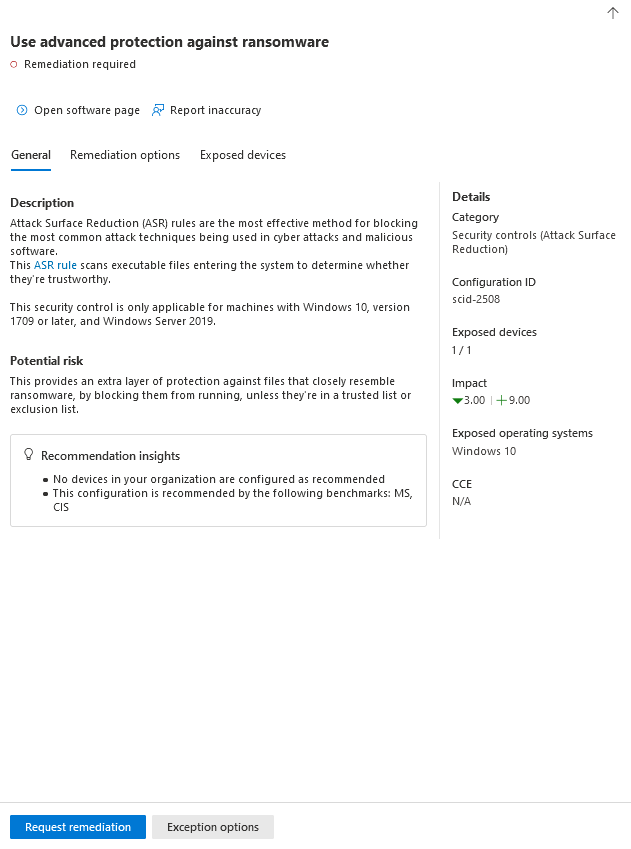
Vulnerabilities exploited in the wild come first. CISA describes its catalog as the authoritative source of these flaws, recommending organizations use it as an input to their prioritization.
Flaws actively used by attackers are flagged first using the CISA KEV catalog.
Exploit Prediction Scoring System scores assign a probability between 0 and 1 that a flaw will be exploited.
Critical systems and exposed devices receive higher priority during remediation efforts.
Scanning finds known signatures, while testing involves human validation. CloudCentric offers separate penetration testing services.
Devices leaving your office remain checked because scanners keep monitoring when laptops are away from corporate networks. Unmanaged Windows machines are reached with credentials. Call to review reports and map out your next steps.
Vulnerability scans check your computers against public lists of known flaws. CVEs are public identifiers for specific known flaws in products, letting flaws be tracked across scanners and vendors.
Scans list known signatures without confirming they are real or exploitable, resulting in false positives. Penetration tests are led by a person who validates findings and chains them together.
Flaws actively exploited in the wild are flagged first using the CISA Known Exploited Vulnerabilities catalog. Each CVE carries a probability score for exploitation to prioritize work.
Built-in and agentless scanners keep monitoring devices even when disconnected from corporate networks. Unmanaged Windows devices are also scanned regularly using credentials to reach them remotely.
Scans provide part of the evidence rules or clients ask for. External PCI scans are run by an Approved Scanning Vendor; confirm requirements with your acquiring bank. Call us to discuss.
Exposures feed straight into patching. Fixes are sent as remediation tasks to Microsoft Intune or blocked when no fix exists. Fix times are not stated here; call to discuss rapid patching.
Microsoft Defender Vulnerability Management delivers visibility and assessments for Windows, macOS, Linux, Android, iOS and network devices. Prices and device limits are not stated here, so call to discuss your environment.
Call CloudCentric to review your device inventory and see where your systems stand.