SOC 2 readiness
SOC 2 compliance preparation for service organizations
CloudCentric gets your business ready for a CPA firm's examination with technical controls in place and evidence kept secure.
Division of labor
SOC 2 readiness separates preparation from examination
CloudCentric manages your technical setup and collects evidence on your systems. A licensed CPA firm reviews your organization against AICPA attestation standards to issue your report.
CloudCentric preparation
- Prepares your business systems
- Puts technical controls in place
- Keeps necessary evidence ready
CPA firm examination
- Independent and licensed CPA firm
- Examines under AICPA attestation standards
- Issues your final report
Organizations needing a SOC 2 report
Customers ask vendors for proof of security and availability. CloudCentric implements controls across systems to help service organizations prepare for external audits.
Common service organizations
Technical controls for your systems
CloudCentric configures your environment to capture proof of security and availability. Systems run silently while generating logs for external auditors.
Cards show controls CloudCentric puts in place while your CPA firm decides what it tests.
Microsoft screens hold your compliance evidence
Microsoft 365 screens show your active technical controls. Compliance Manager keeps owners, status and evidence organized per improvement action and exports assessments for external auditors.
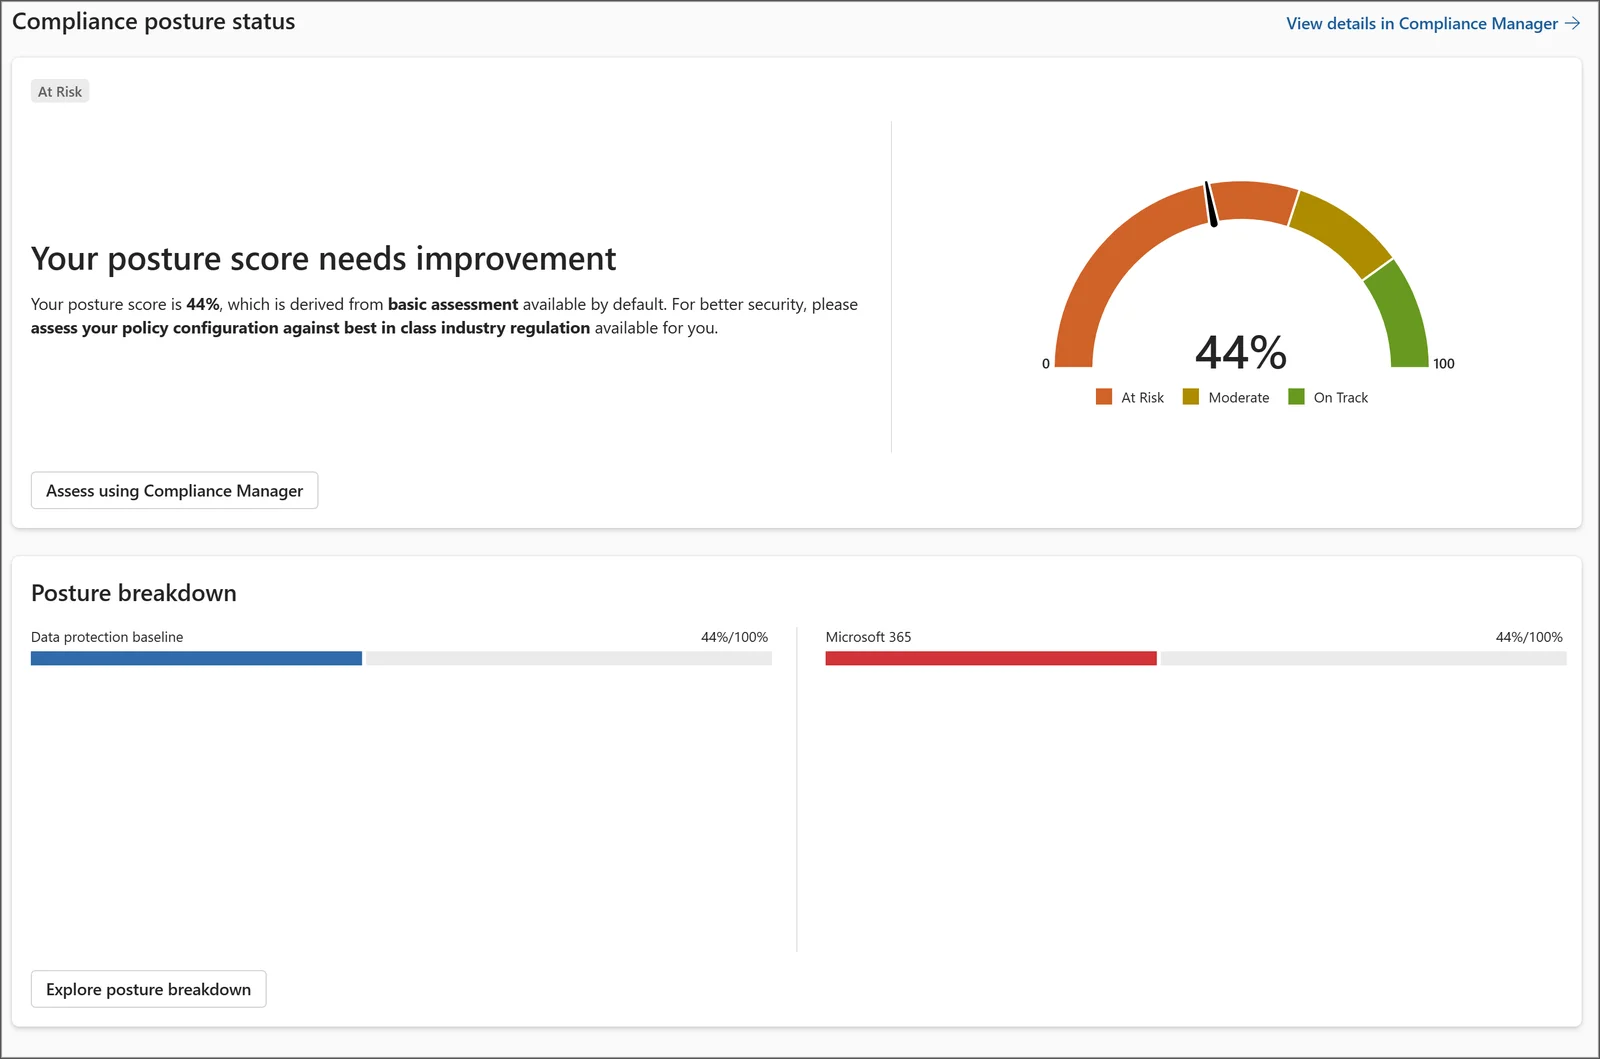
Purview compliance posture card displays your score and offers an Assess using Compliance Manager button.
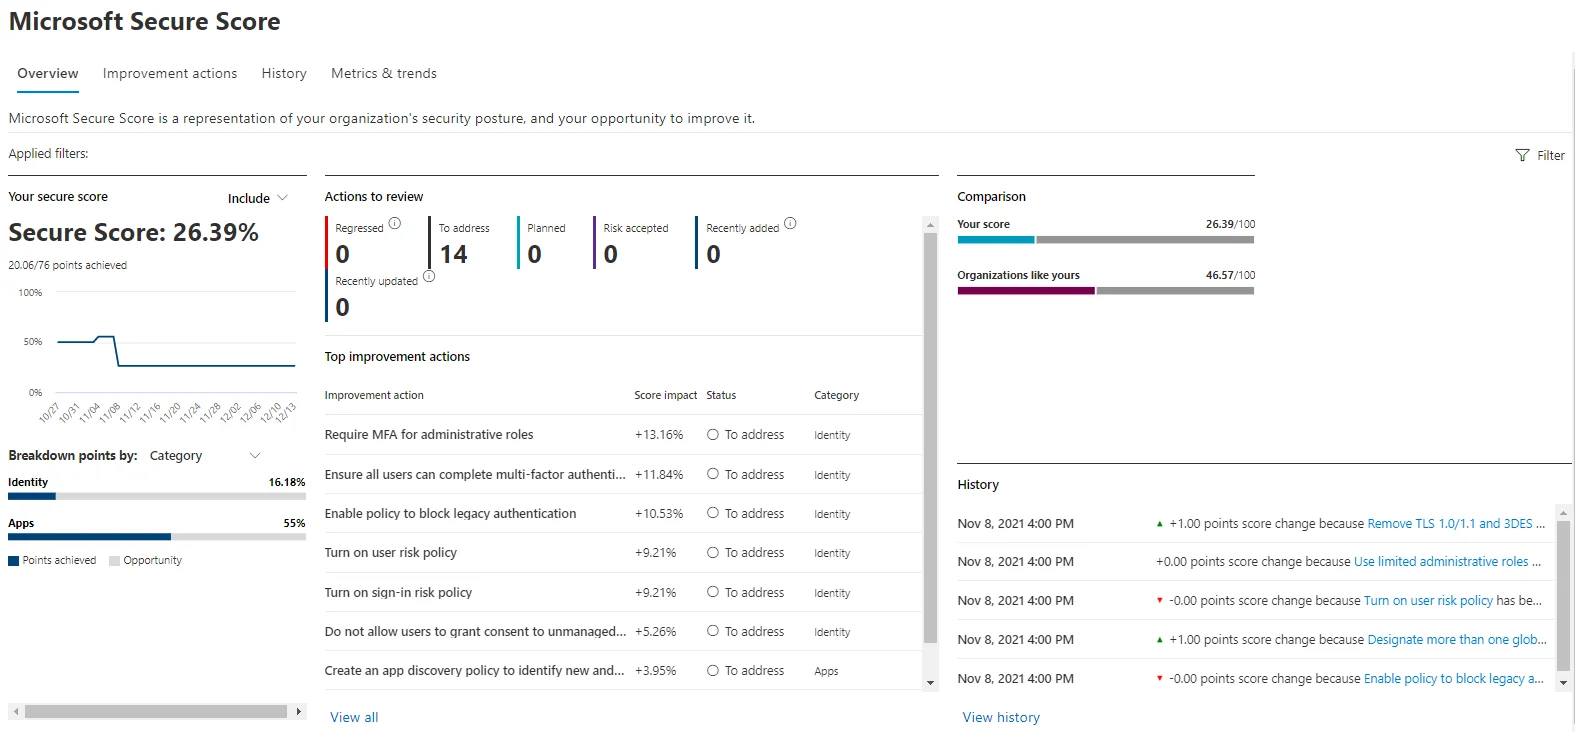
Secure Score overview measures your security posture and provides a direct comparison with similar organizations.
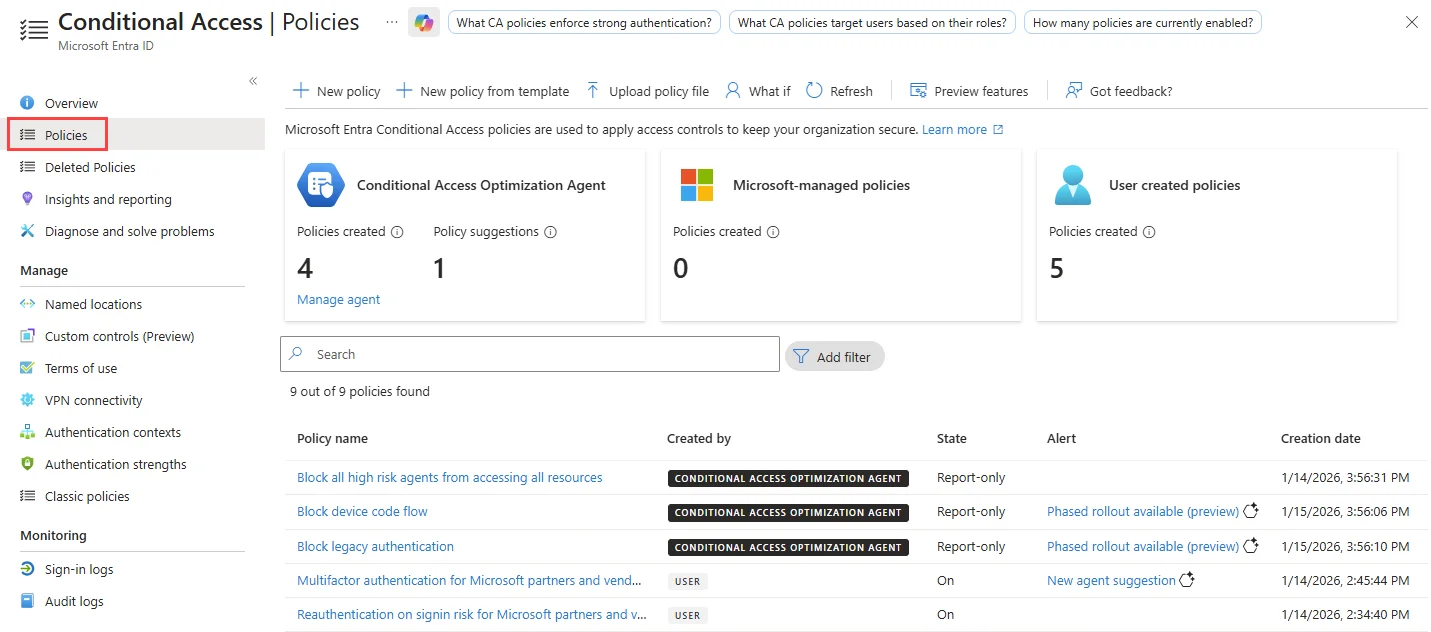
Conditional Access policies list shows active rules governing user sign-ins and device compliance checks.
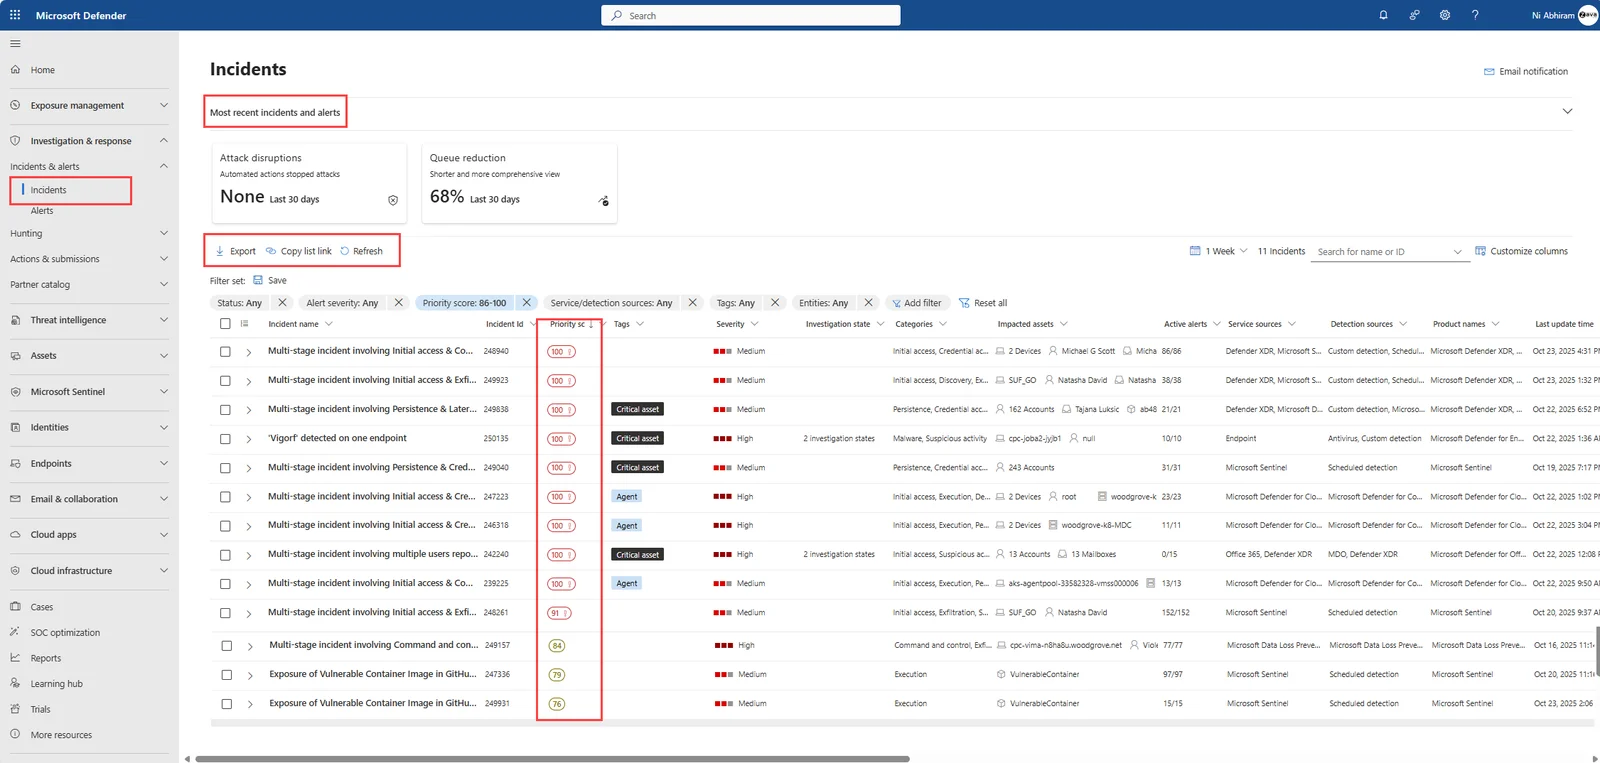
Defender incident queue organizes security alerts for immediate review and systematic ticket tracking.
Screenshots display Microsoft's own samples sourced directly from Microsoft Learn documentation.
SOC 2 preparation follows a logical sequence
Preparation requires mapping your existing systems to established criteria before external reviews begin.
- 1
Agree scope with CPA firm
Organization owners decide with a licensed CPA firm which of five trust services categories the final report covers.
- 2
Check current technical controls
CloudCentric evaluates your existing environment against required controls to identify gaps in security or availability.
- 3
Put controls in place
Engineers implement technical policies across Microsoft 365 to enforce access rules and protect sensitive data.
- 4
Document and collect evidence
Compliance Manager tracks improvement actions and holds uploaded evidence files or links securely on its Evidence tab.
- 5
Hand evidence to CPA firm
Assessments export to Excel files to provide snapshots for external auditors performing your examination.
Common questions about SOC 2 readiness
- Who performs a SOC 2 examination and issues the report?
A licensed, independent CPA firm performs the examination under AICPA attestation standards and issues your final report. CloudCentric prepares your business but does not audit or issue reports.
- Is SOC 2 a certification?
SOC 2 is an assertion-based examination, not a certification. CloudCentric does not certify anyone. A CPA firm evaluates controls relevant to your selected categories and provides an assurance report.
- Which of the five categories does the report cover and who decides?
Your company and your CPA firm decide which categories apply. Categories include security, availability, processing integrity, confidentiality or privacy. CloudCentric does not make this decision.
- What does CloudCentric do before the examination?
CloudCentric prepares your business by putting technical controls in place on your systems, documenting how each control works, and keeping evidence ready for your CPA firm.
- Is Microsoft 365, Secure Score or Compliance Manager alone enough?
Microsoft products do not produce a SOC 2 report or make a business compliant on their own. They help manage compliance and store evidence files for external auditors.
- Which criteria edition applies now and what is the proposed 2027 update?
Current examinations use the 2017 trust services criteria and 2018 description criteria, both with 2022 revisions. The AICPA proposed an exposure draft for 2027 criteria; if approved, they apply after December 31, 2027.
Prepare your service organization for examination
Book a walkthrough to review technical controls and start organizing your compliance evidence.