Security posture review
Charleston cybersecurity risk assessment services
CloudCentric provides a cybersecurity risk assessment measuring sign-in rules, devices, software and backups against NIST Cybersecurity Framework 2.0 for businesses from Charleston to Savannah.
Settings and inventories
Reviewing configurations to rank necessary fixes
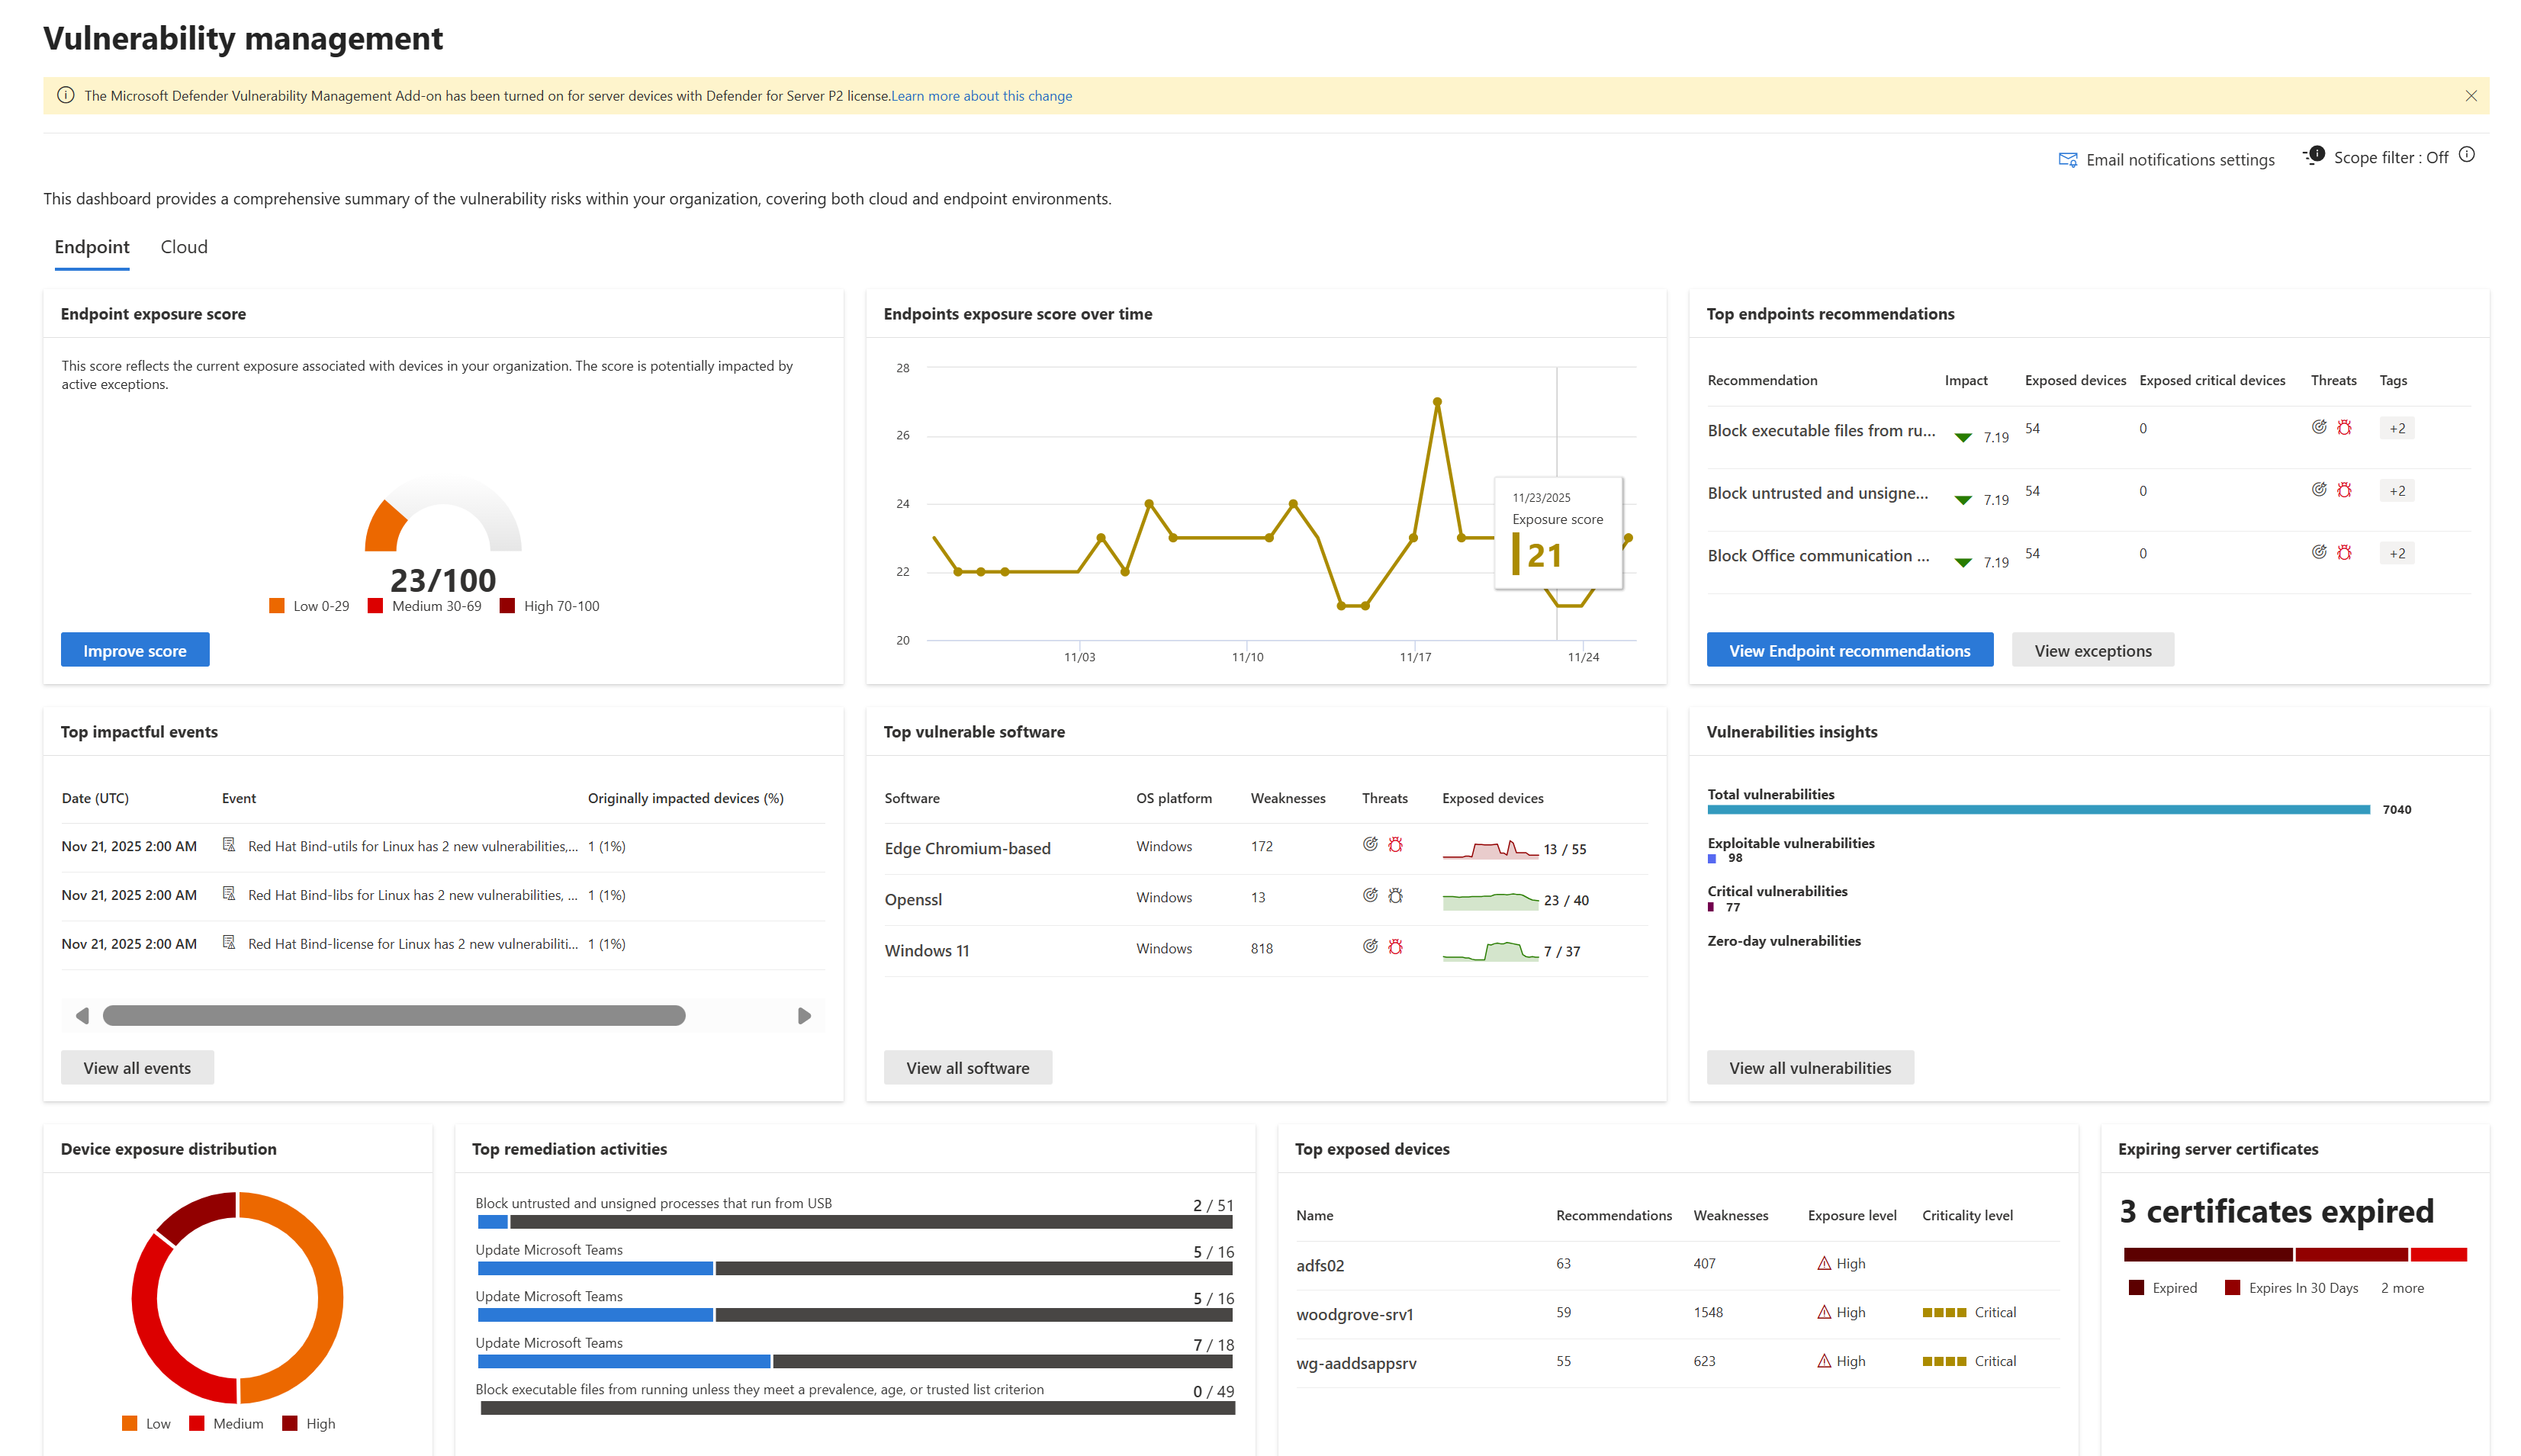
Configuration scores show controls are on, not that they hold. Assessments read settings and inventories to rank fixes. Penetration tests are separate jobs attempting problems.
- 1
Reads your existing settings
Reviewing configurations shows directly how systems operate daily and exposes gaps in sign-in rules, devices and software.
- 2
Measures against published frameworks
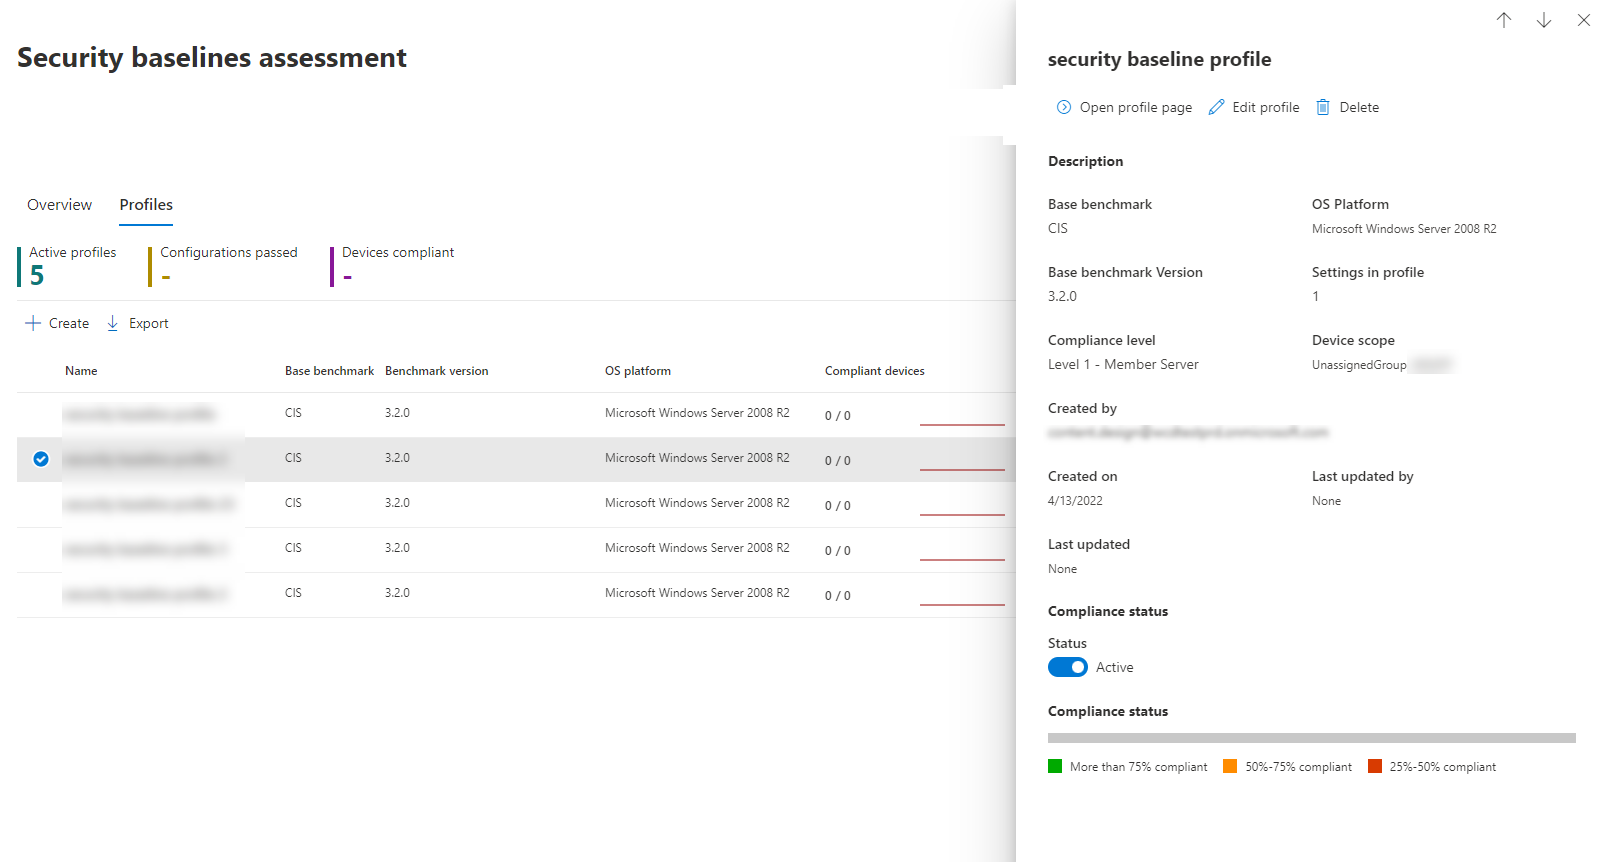
Checking configurations against NIST standards grounds the review in established practices rather than opinion.
- 3
Ranks required fixes first
Ordering recommendations by score impact highlights critical gaps, putting high-value corrections at the top of lists.
NIST Cybersecurity Framework 2.0 functions
NIST announced version 2.0 on February 26, 2024, designing it for organizations of every size and type with six core functions.
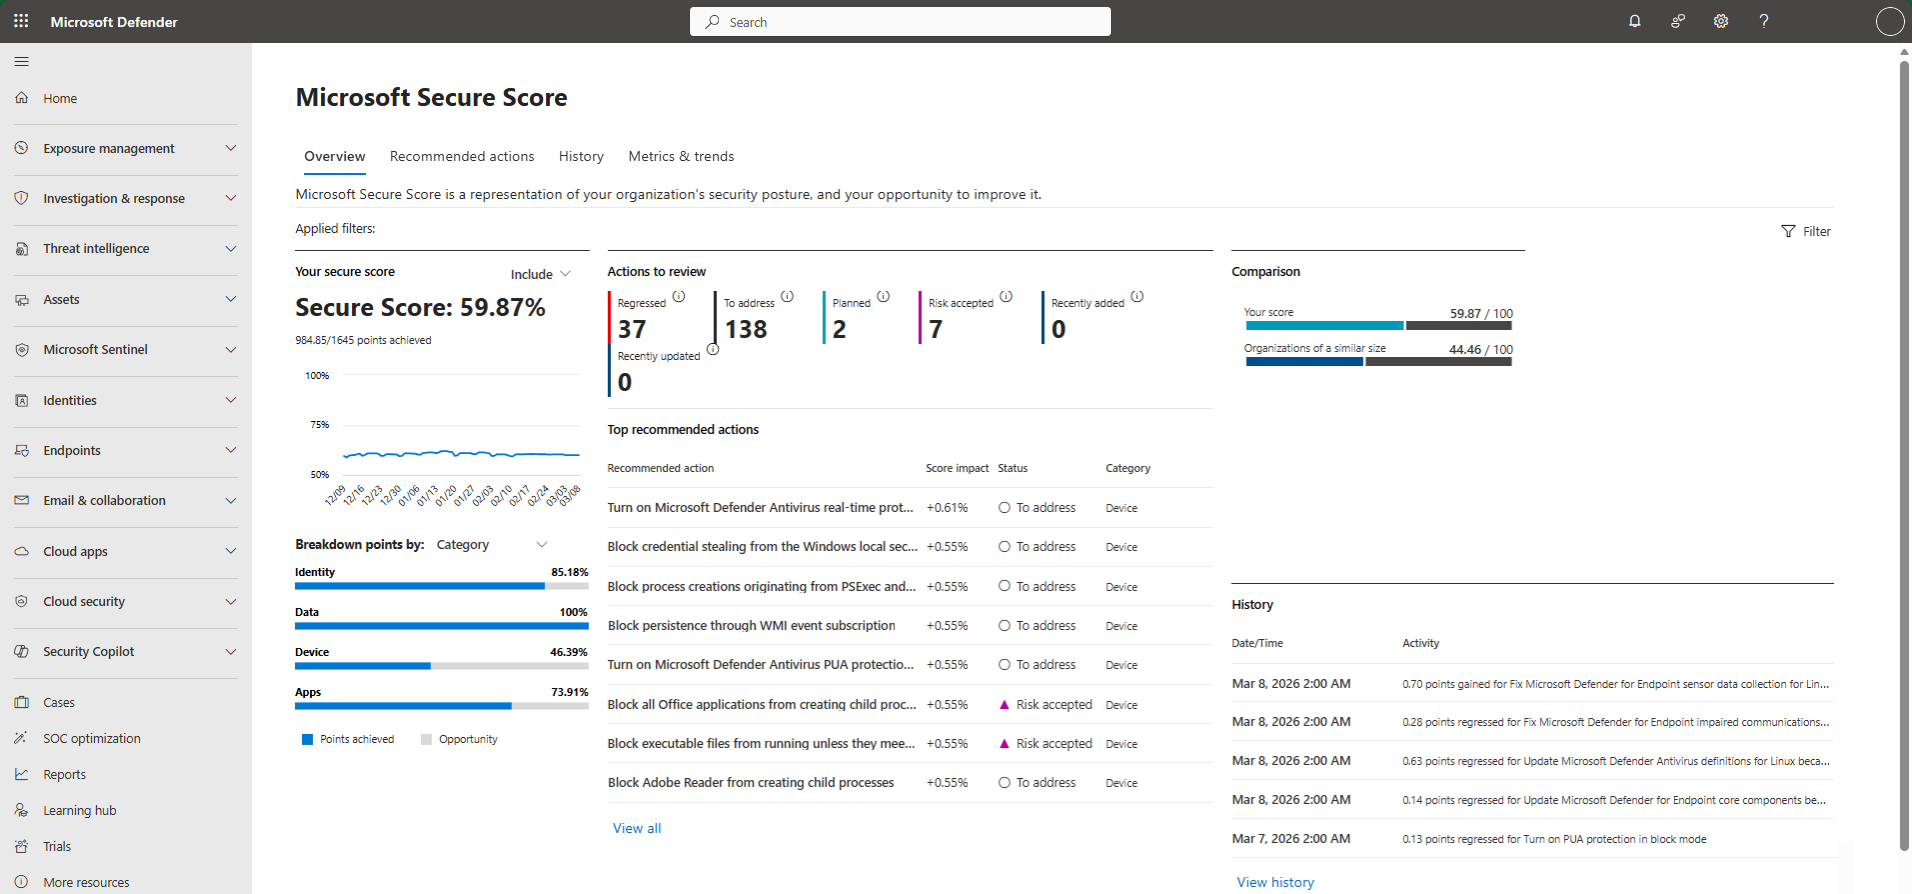
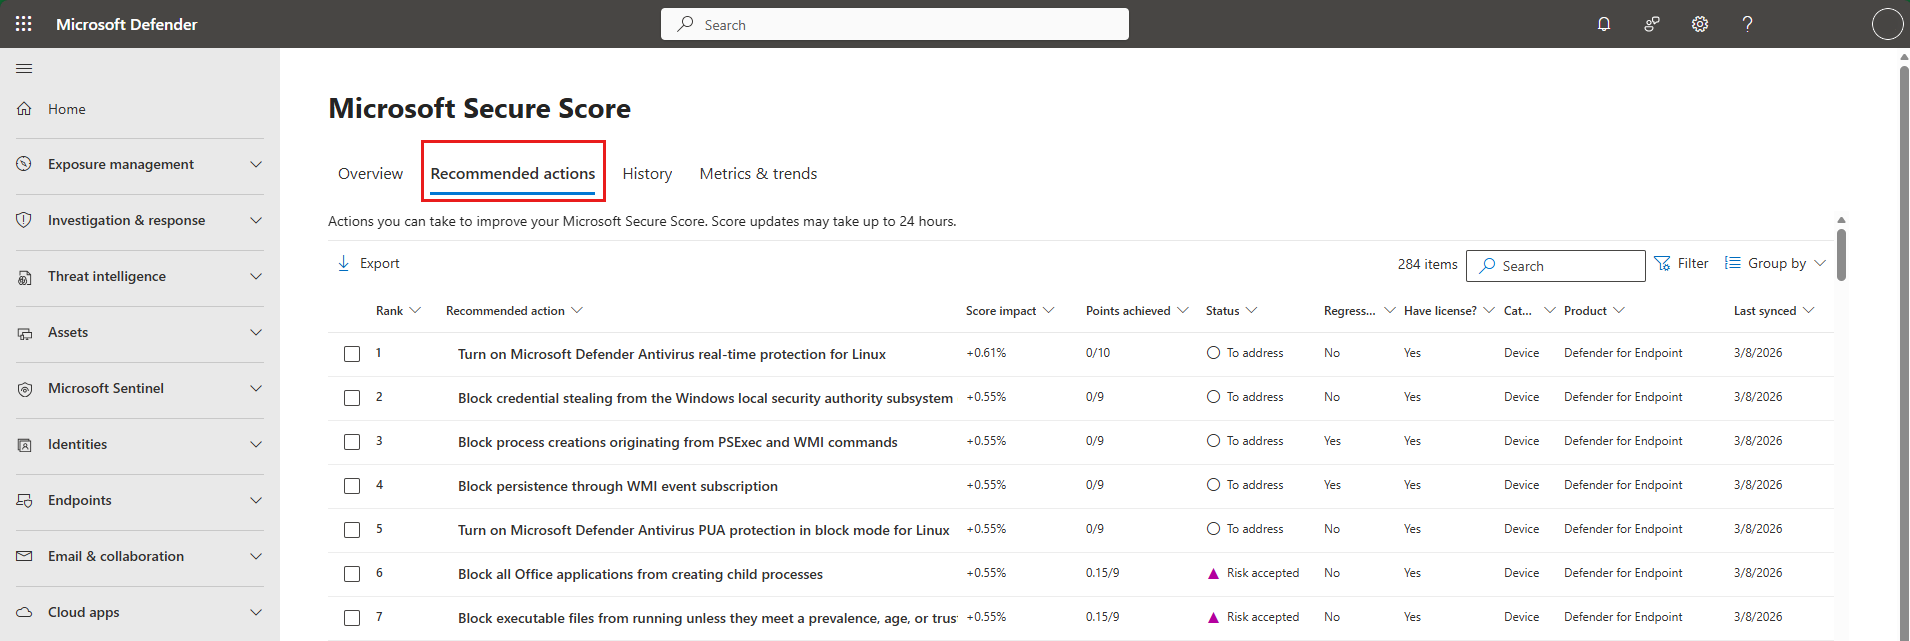
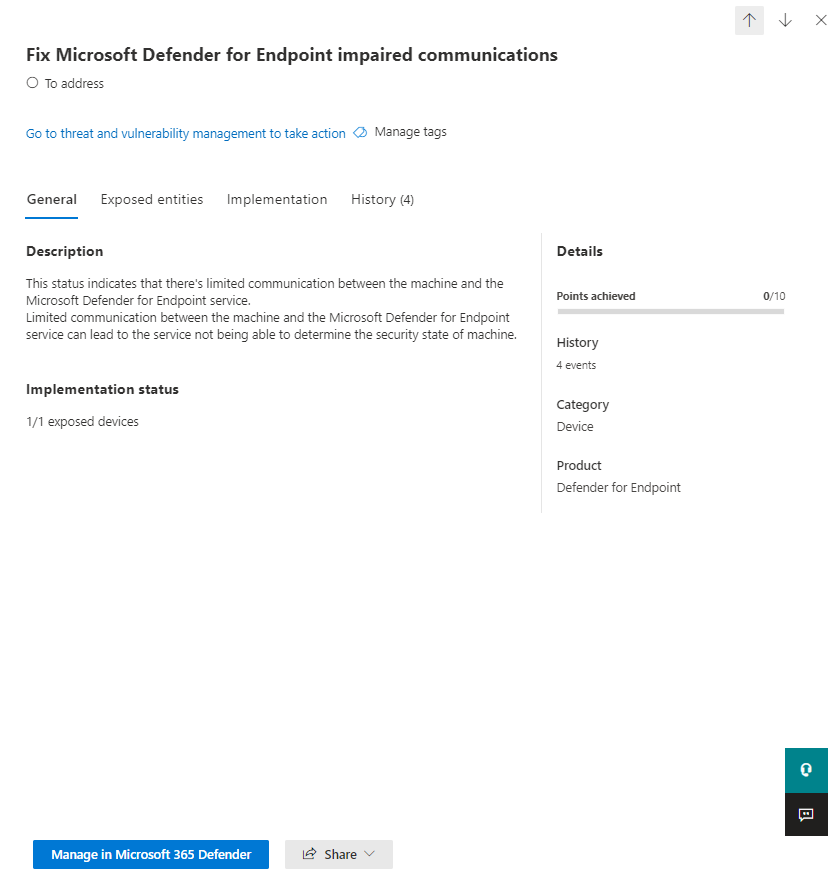
Assessment reads
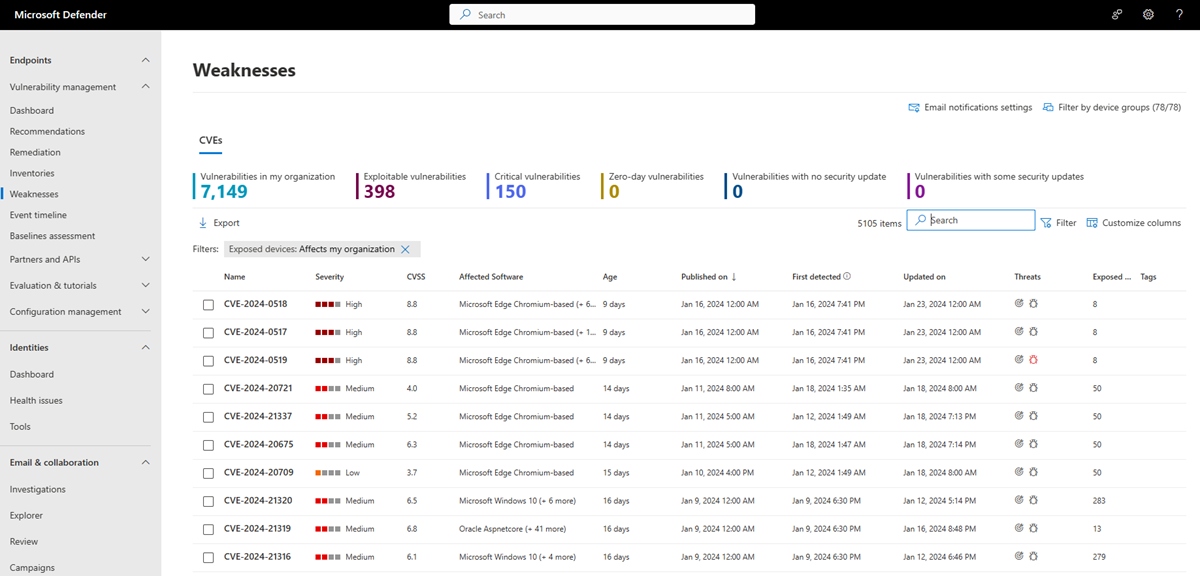
Microsoft security portal screenshots
Microsoft Secure Score measures posture in Microsoft Defender, ranking actions by impact.
Common reasons for needing assessments
Different industries face distinct requirements prompting reviews of their configurations.
Assessment triggers
Assessment steps and example findings
Checking configurations follows a sequence ending in ranked priorities.
- Summary
- Example business findings show missing multi-factor authentication, unpatched software and backups needing separation from Microsoft 365.
Multi-factor authentication gaps Fix first
- Area
- Protect
- Found
- Sign-in rules lack multi-factor authentication for administrators.
- Fix
- Microsoft Conditional Access sets rules requiring multi-factor authentication for sign-ins.
Unpatched software vulnerabilities Next
- Area
- Identify
- Found
- Installed software contains flaws listed in the CISA Known Exploited Vulnerabilities catalog.
- Fix
- Patching applications resolves vulnerabilities flagged by active exploitation.
Deleted email retention Later
- Area
- Recover
- Found
- Exchange Online keeps deleted email for 14 days by default.
- Fix
- Backups stored separately from Microsoft 365 restore items after default windows pass.
Next steps
Fixing findings or confirming with testing
CloudCentric fixes findings through its other security services, or hands over lists. Penetration tests serve as next steps when confirmation by attempt is wanted. Assessments are normal ways to start, not limited to existing clients.
- 1
Fixes through security services
Patching, passwords and sign-in rules address configuration gaps directly.
- 2
Training for behavior items
Addressing behavior items requires training instead of configuration changes.
- 3
Penetration tests
Penetration testing confirms controls hold by attempting problems.
Frequently asked questions
- What is a cybersecurity risk assessment?
Reviews of how business security is set up measure sign-in rules, devices, software, email protection, backups and habits against published frameworks.
- How does an assessment differ from a scan or penetration test?
Assessments read settings and inventories. Penetration tests are different jobs where people work within scopes to reach further into systems and confirm problems by attempting them.
- Is a cybersecurity assessment the same as a cyber security audit?
Frameworks sometimes require formal audits or assessment reports. Outside firms perform them and issue reports. CloudCentric prepares businesses for them and puts technical controls in place.
- Does an assessment cover the network and network devices?
Microsoft Defender Vulnerability Management covers network devices and checks them against the public list of known vulnerabilities with the same ranked list.
- What is NIST Cybersecurity Framework 2.0 and who is it for?
NIST announced version 2.0 in February 2024. NIST designs it for all audiences, industry sectors and organization types, describing quick-start guides for specific users like small businesses.
- Can a business that is not an existing client ask for an assessment?
Assessments are normal ways to start with CloudCentric and are not limited to existing clients. Costs and timing are settled in scoping, so call to discuss.
- Does an assessment satisfy HIPAA, the Safeguards Rule, PCI or an insurer?
Assessments produce material for them. Businesses confirm what applies with their assessors, insurers, acquiring banks or counsel.
Call to discuss scoping
Book a walkthrough or call (844) 422-7000 to start reviewing configurations.