AI governance program
AI governance for professional offices
Staff already use public AI tools, so a governance program outlines approved tools and gives them a supported route inside your own tenant.
Governance in practice
See approved tools and secure your workflow
Your team likely uses public AI tools to draft and summarize. A governance program states approved uses, gives staff an approved route for their work, and shows exactly which AI tools are active across your network.
- 1
One-page acceptable use policy
A clear document outlining approved tools, allowed materials, and review requirements before output leaves the office.
- 2
List of AI tools seen
Discovery shows consumer AI use through browser activity and inventories AI apps registered in your directory.
- 3
Approved assistant inside Microsoft
An approved assistant runs inside your business's own Microsoft 365 tenant, with every single request logged securely.
AI governance across different professions
Professional offices handle sensitive client files daily. A structured policy ensures staff know exact boundaries for AI tools while handling protected material.
Select your business type
Related service pages
Scenarios in your AI usage policy
Everyday tasks require clear guidelines. Your governance program addresses common situations directly, providing a clear boundary for staff and a secure alternative for daily work.
Choose a scenario
Current behavior
Approved route
Policy guideline
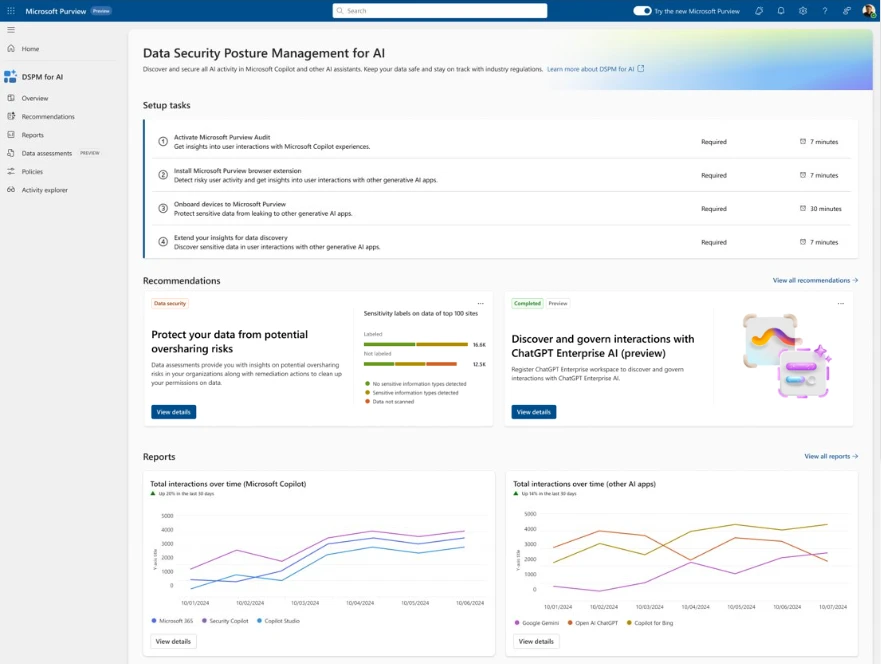
Uncover shadow AI across your network
Discovery uses Microsoft governance tooling to detect consumer AI use through browser activity and inventory registered apps. Spotting visits requires the browser extension, helping you evaluate shadow AI clearly.
Copilot experiences and agents
Reports group activity into Microsoft Copilot and agents such as Copilot Studio actively used within your environment.
Enterprise AI apps registered
Inventory highlights enterprise applications that are registered directly against your local directory.
Other AI apps detected
Supported third-party AI sites reached in a browser are detected and categorized.
Core elements of an AI acceptable use policy
A practical AI policy fits on one or two pages. Because available tools change month to month, your policy names an owner who reviews guidelines on a set cadence.
Approved tools list
Clear guidelines state exactly which AI platforms are authorized for business use. An assigned owner reviews this list regularly.
Approved material categories
Staff receive boundaries on the specific files and data types each tool may receive, keeping sensitive client information secure.
Review before material leaves
Guidelines define exactly what a person reviews and verifies before any model-drafted material leaves the firm.
Designated points of contact
Employees always know exactly who to ask regarding new agents, third-party add-ins, or questions about acceptable use.
Microsoft documentation:DSPM for AI,Auditing Copilot and AI apps.
Implement your AI governance framework
Getting started takes a structured approach. Firms often combine this framework with a readiness assessment, in either order, to establish secure operations.
- 1
Discovery across the tenant
Discovery covers your tenant, browsers, and registered directory apps to find active tools. Setup takes days rather than weeks.
- 2
Draft the one-page policy
Create a concise acceptable use policy covering approved tools, material boundaries, and required reviews for generated output.
- 3
Set up approved assistants
Deploy a supported route inside your own Microsoft 365 tenant, ensuring every prompt and response is logged securely.
- 4
Set cadence and owner
Assign a dedicated owner to review your policy on a regular schedule, managing month-to-month changes in available AI tools.
Common questions about AI governance
- Does blocking AI sites work on its own?
Blocking consumer AI tools on their own tends not to hold. Approving a route that does the same work inside your tenant and blocking unapproved sites narrowly is the recommended approach.
- What does discovery cover?
Discovery covers your Microsoft tenant, browsers, and an inventory of AI apps registered against your directory. Detecting browser activity requires devices to be onboarded properly.
- What does Microsoft's weekly data risk assessment check?
Default assessments run weekly across your top hundred SharePoint sites by usage. Summaries highlight items found, items containing sensitive data, and active links sharing data with anyone.
- Are all of these Microsoft tools included in every plan?
Discovery, endpoint data controls, and compliance tools are not uniformly included in mid-market plans. Entitlement is checked per capability rather than assuming a set bundle.
- Are prompts and responses recorded in the approved assistant?
Prompts and responses are captured in the unified audit log and stored in the user's mailbox. Logs can be discovered later to review interactions securely.
- Who reviews the policy after it is written?
A designated owner handles ongoing reviews on a set cadence. Deciding which tools and vendors are allowed is an ongoing task because available options change month to month.
Book a conversation about AI governance
Call (844) 422-7000 or book a conversation to establish secure AI boundaries for your staff today.